Blog
Insights on ISO 42001, ISO 27001 and EU compliance.
Practical articles for CISOs, security officers and IT managers on AI governance, information security, NIS2, DORA and choosing the right tools.
01 / Articles
All articles.
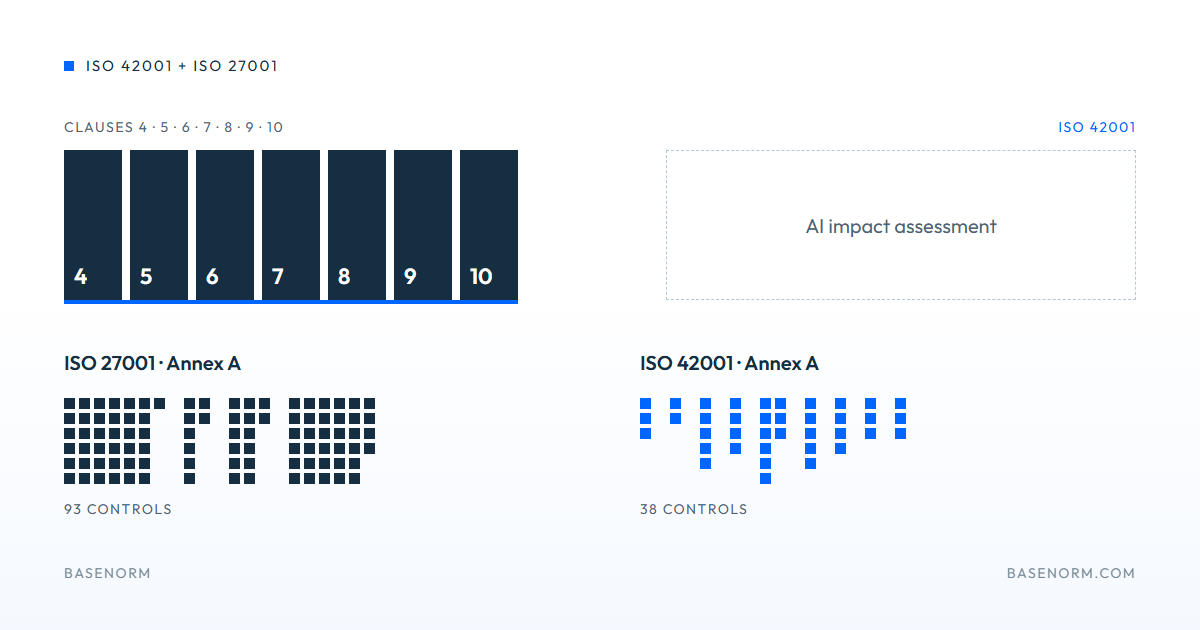
Adding ISO 42001 to ISO 27001: what you can reuse, and what is genuinely new
When the EU pushed back the high-risk deadlines of the AI Act this summer, many organisations heard a reason to wait. The better reading is the opposite: there is now time to build AI governance properly, before the obligations bite. For organisations that already run an ISMS, ISO 42001 is the obvious vehicle, and a good part of the work is already done.
4 min read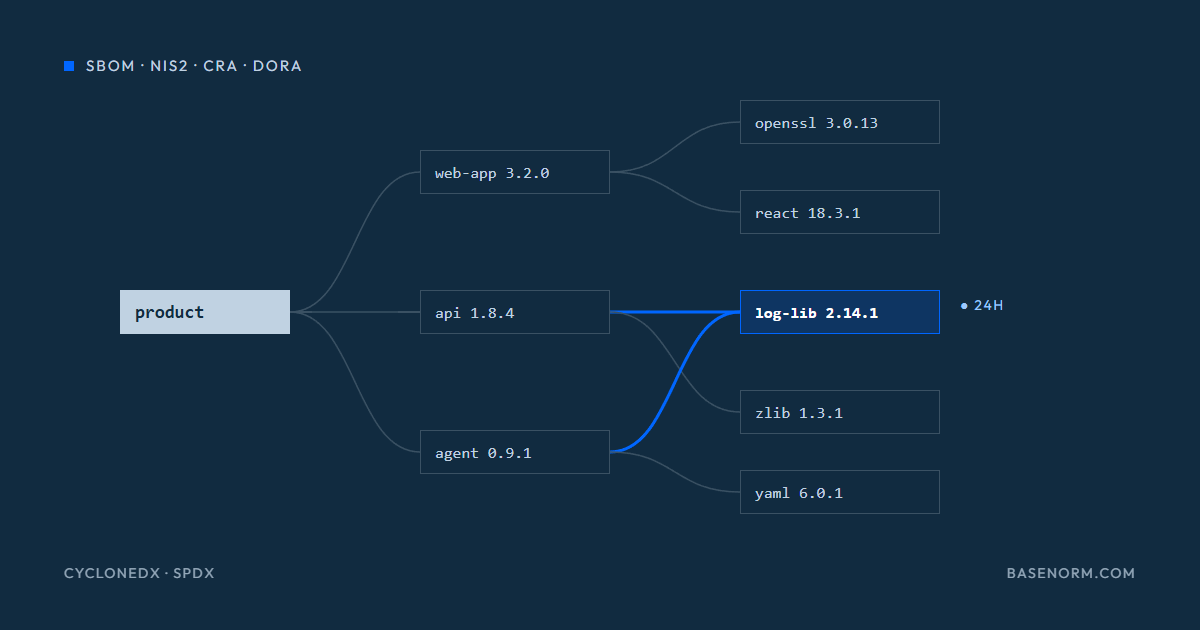
SBOMs under NIS2, the Cbw and the CRA: what is actually required, and from whom
Within four weeks this summer, two obligations started to apply. The Dutch Cyberbeveiligingswet entered into force on 15 August 2026, and the reporting obligations of the Cyber Resilience Act apply from 11 September 2026. Both bring the same question back to the table: do you know which software components run in your systems, and in the products you sell?
4 min read
Compliance on autopilot? Why AI should assist your management system, not run it
A new generation of compliance tools promises that AI agents will collect your evidence, judge your controls and close your gaps without anyone lifting a finger. It is an attractive pitch for a stretched security team. It also misunderstands what a management system is for.
3 min read
The platform behind your ISMS is a supplier too: what NIS2 and DORA mean for where your compliance data lives
Since 15 August 2026 the Dutch Cyberbeveiligingswet, the national implementation of NIS2, applies to some 8,000 organisations. Supply chain security is one of its core obligations. Most security teams think first of their cloud providers and software vendors. Fewer think of the platform where they keep their risks, incidents and vulnerabilities.
3 min read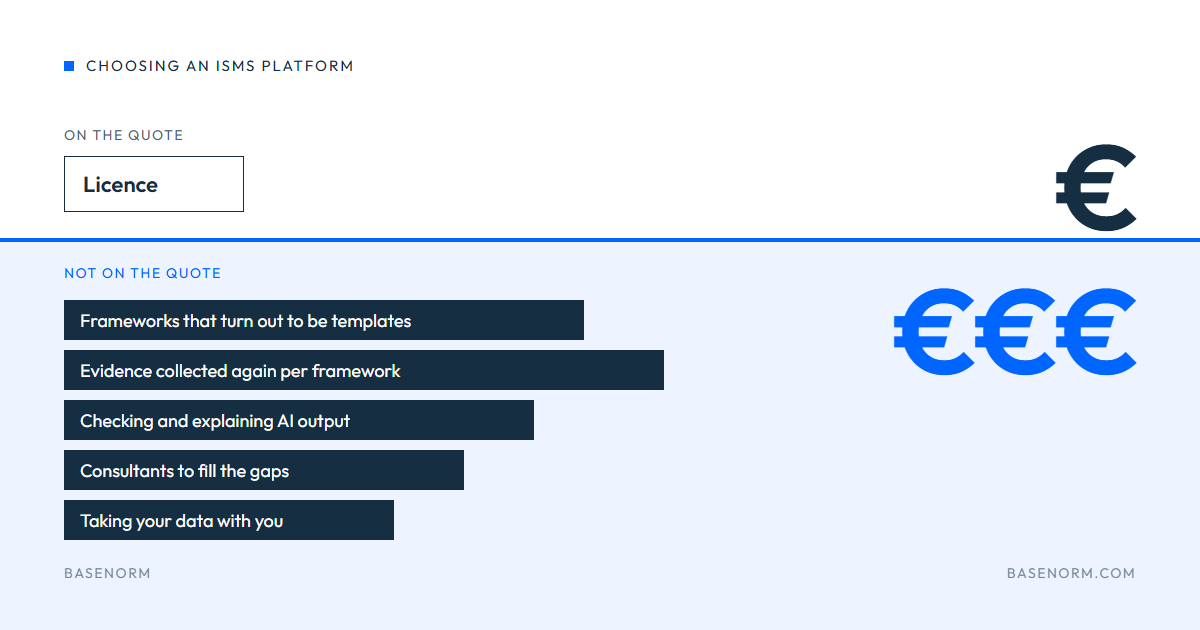
Choosing a platform for your ISMS: the costs that do not appear on the quote
The licence fee of a platform for your ISMS, often sold as GRC software, is easy to compare. What it costs to work with the tool for three years is not. Those costs sit in frameworks that turn out to be templates, evidence that has to be collected again for every standard, AI output that someone has to check, and data that is hard to take with you. They become visible only after the contract is signed, unless you ask the right questions first.
4 min readBook a demo
See it in your own context.
In a demo we look at your frameworks, your controls and your next step.
- Where you stand with ISO 27001 and ISO 42001.
- Which frameworks apply to you.
- How AskNorman fits your team.
Hosted in the Netherlands. Your data stays in the EU.